
Company
We built the platform we could not find.
Sentrix was founded in Montréal by GRC practitioners. Our story, the principles behind the platform, and the team that builds and supports it every day.
Sentrix was founded in Montréal by a team that spent years running GRC programs at regulated financial institutions and scaling SaaS companies. We kept buying the same tools, mapping the same controls in different spreadsheets, and running the same evidence sprint every quarter. There had to be a better way.
The problem we set out to solve
A mid-market enterprise typically runs several separate GRC tools. They do not talk to each other. Evidence is collected several times. Controls are mapped several times. And then the renewal invoices arrive, each one unchallenged because nobody has the time or the data to push back.
We quantified this for our first customers: the same capability — policy management, evidence collection, control tracking — paid for in several applications at once.
Law 25, CPCSC and TGV were rarely supported natively by the platforms we evaluated. For the regulated enterprises and public-sector suppliers we were building for, this was not acceptable.
Sentrix was built to fix all of it: one platform for compliance automation, third-party risk, policy management, license governance and integrations, with Canadian, American and European frameworks supported from day one.
Where we are today
We are headquartered in Montréal, Québec, Canada, and our customers operate in Canada, the United States and Europe. We are building for the long term, not optimizing for growth-at-all-costs metrics that create the wrong incentives in a compliance-critical product.
Our principles
Evidence over claims
We do not ask customers to trust our compliance posture. We show it. The controls we operate are documented on our Security page, and our sub-processors are listed in our Privacy Policy.
Native to Canadian frameworks. Built for international ones too.
Law 25, CPCSC and TGV are native. So are SOC 2, HIPAA, CMMC, GDPR, NIS2 and DORA, because our customers operate in Canada, the United States and Europe.
The platform should pay for itself
Every customer engagement starts with a license optimizer analysis. We show you exactly what your current GRC stack costs and what you can cut. Sentrix should save you more than it costs you before your first audit closes.
Customer success is included
GRC platforms that require a paid implementation engagement to go live have misaligned incentives. Sentrix is self-guided. Implementation services are optional, never a prerequisite, and customer success is included, not billable.
Built by people who live and breathe GRC.
William Georges Khouri — President & Founder
CISSP, CISM and ITIL certified, William founded Sentrix to bring GRC automation to regulated organizations and leads the company's strategy, product vision and market expansion.
Fanny Le Jeune — Financial & Administrative Director
Fanny is part of the leadership team and oversees finance, administration, human resources, legal matters and selected marketing initiatives, bringing the financial discipline and transparency that clients in regulated sectors expect.
Jorge Seara — Account Manager
Jorge supports Sentrix clients in adopting and using the platform, drawing on several decades of experience in client support to make sure they get the value delivered and build a lasting relationship based on trust.
See what we built.
A demo using your real infrastructure. No slides. No hypotheticals. Contact us.
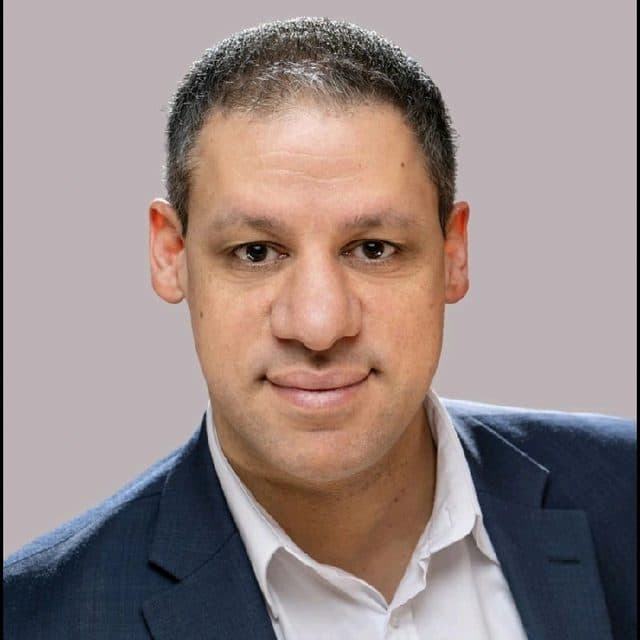
William Georges Khouri
President & Founder
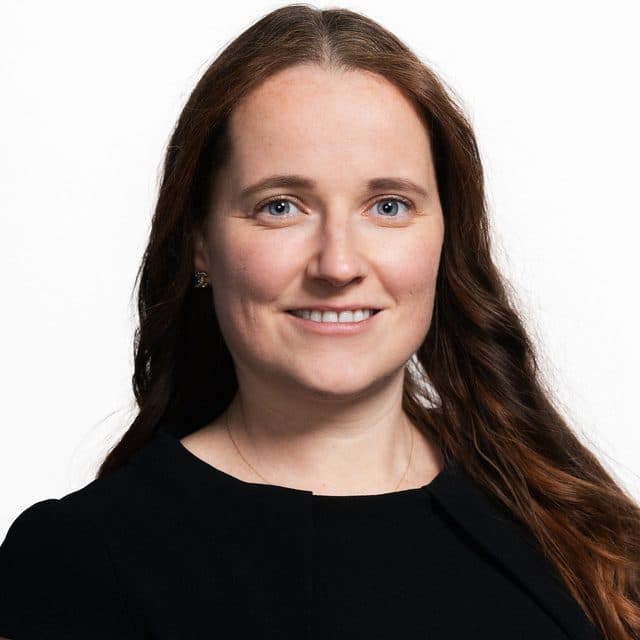
Fanny Le Jeune
Financial & Administrative Director
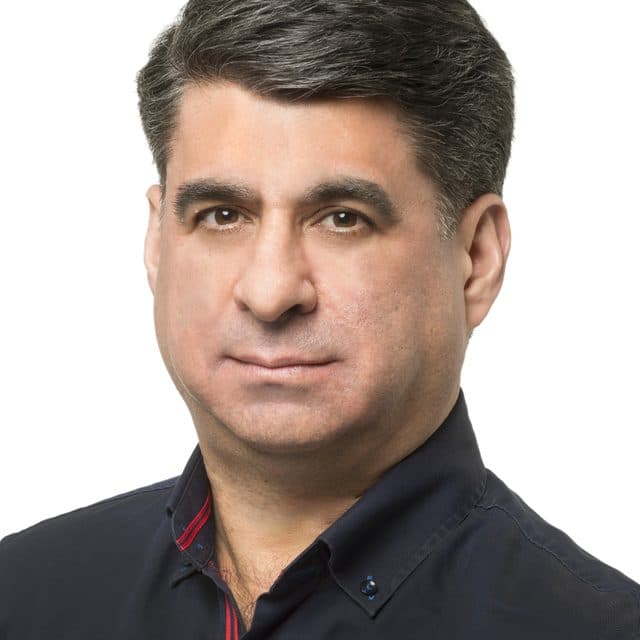
Jorge Seara
Account Manager
Frequently asked questions
- Where is Sentrix based?
- Sentrix is headquartered in Montréal, Québec, Canada. It was founded there by a team that spent years running GRC programs at regulated financial institutions and scaling SaaS companies, and it now serves customers operating in Canada, the United States and Europe from that base.
- Which frameworks does the platform support natively?
- Law 25, CPCSC and TGV are native to the platform. So are SOC 2, HIPAA, CMMC, GDPR, NIS2 and DORA, because Sentrix customers operate in Canada, the United States and Europe and rarely have to satisfy a single jurisdiction. Canadian, American and European frameworks are handled at the same level.
- Do we need professional services to go live?
- No. Sentrix is self-guided and customer success is included rather than billed. Implementation services exist for organizations that want them, but they are optional and never a prerequisite. Every engagement starts with a license optimizer analysis of what your current GRC stack costs and what you can cut.
- Who is on the Sentrix team?
- The company is led by William Georges Khouri, President and Founder, who is CISSP, CISM and ITIL certified. Fanny Le Jeune, Financial and Administrative Director, oversees finance, administration, human resources and legal matters. Jorge Seara, Account Manager, supports customers in adopting and using the platform.
Related pages
Company
Grow your GRC practice with Sentrix.
Three ways to partner with Sentrix: audit and assurance firms, GRC consultancies and MSSPs, technology resellers and integrators. Built for depth, not volume.
Contact
Let's talk about what you need.
Ask for a live demo or help with implementation and ongoing compliance work. A real person reads every request and connects you with the right specialist.
Security
How we protect your compliance data.
The controls Sentrix operates continuously: encryption, least-privilege access, read-only integrations, incident response and responsible disclosure.
Let's talk about your compliance program.
Last updated: 2026-09-17